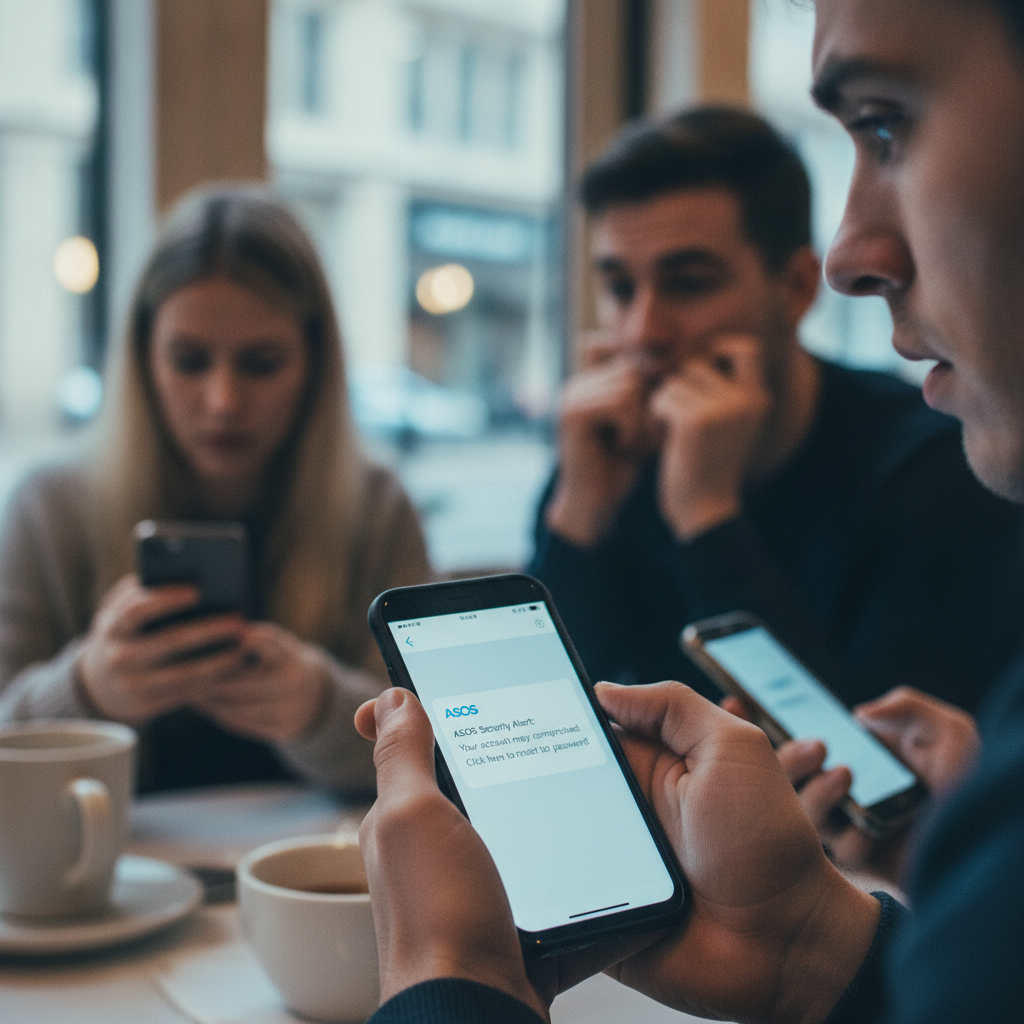
ASOS users across the UK have received pop-up notifications from the retailer’s app that appeared to have been sent by hackers attempting to extort the company.
What happened
The messages were delivered through the ASOS app and appeared as pop-up notifications to users. Their apparent origin raised concerns that the retailer’s customer-facing platform had been used to distribute communications not sent through normal ASOS channels.
The available information does not specify how many users received the notifications, what the messages contained or whether customer data was accessed. It also does not provide details of any response from ASOS.
Why the messages matter
For a major online retailer, unexpected messages appearing inside its app can create uncertainty for customers and draw attention to the security of its digital communications. The apparent attempt to extort ASOS also adds a business dimension beyond a routine technical disruption.
At this stage, the notifications are described as appearing to have been sent by hackers. That does not establish the full nature or extent of any unauthorised access, and no further technical details are available from the source information.
What is known so far
The incident affected ASOS app users across the UK. Beyond the reported pop-ups and their apparent connection to an extortion attempt, the source provides no confirmed information about the perpetrators, the company’s systems or the outcome.
The episode highlights how incidents involving mobile apps can quickly reach customers directly, even when the underlying facts remain unclear.